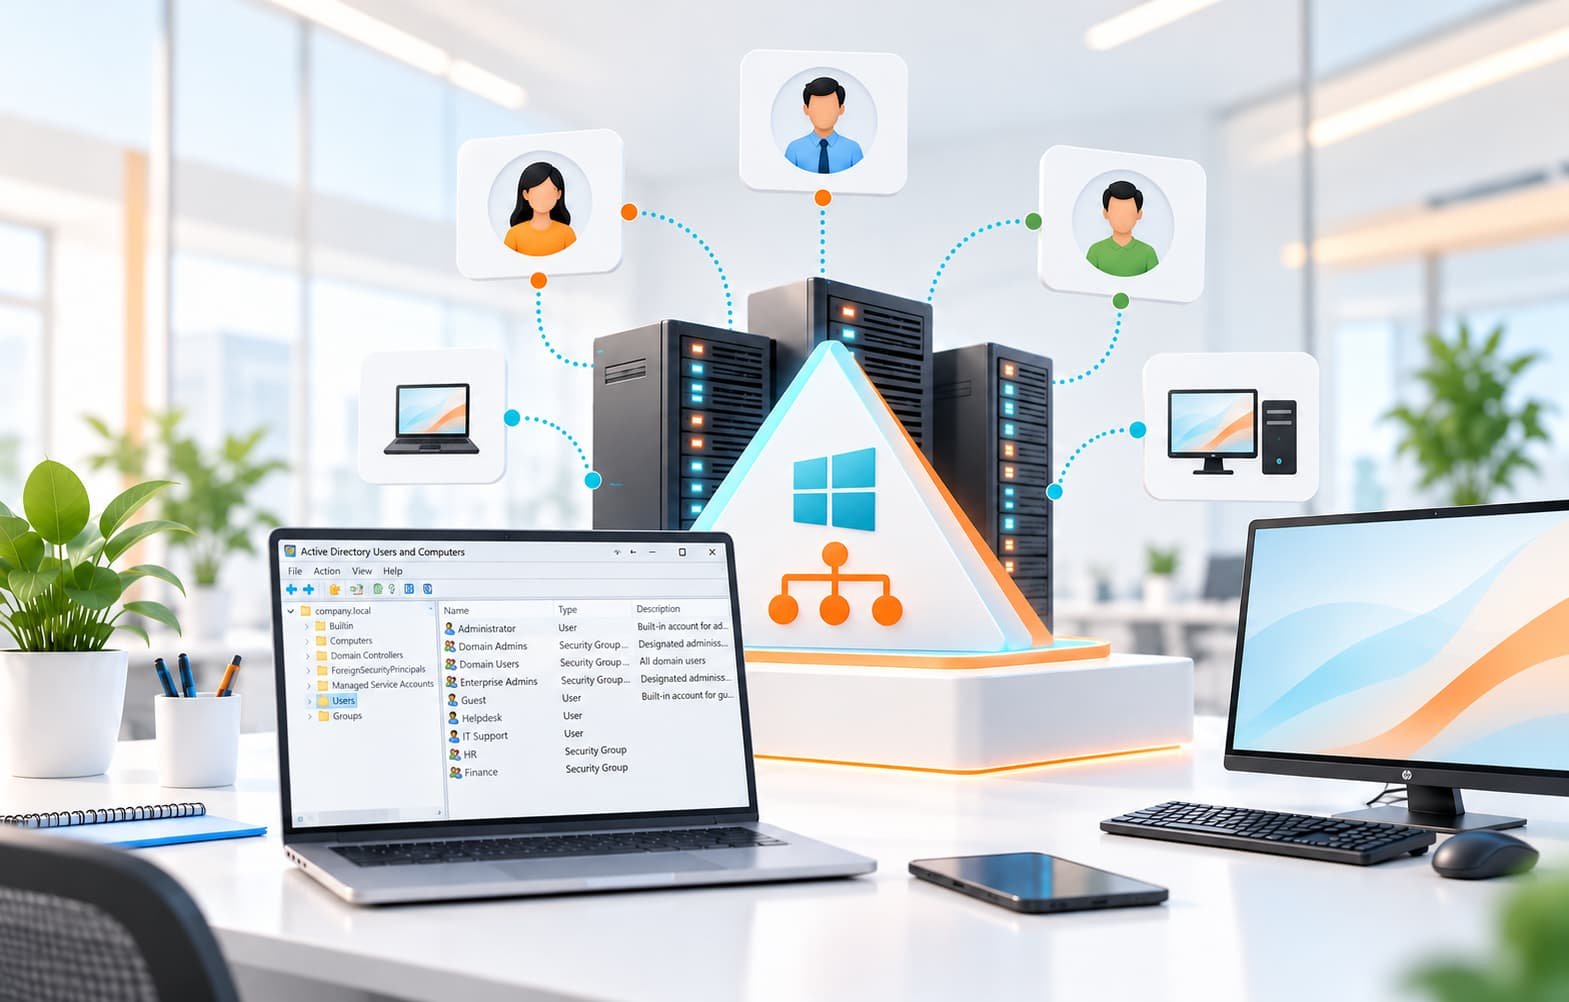
One login for your team. One audit trail for every access.
Connect KOŚA to your Active Directory, LDAP or SSO provider. Manage users and roles centrally, enforce MFA and show inspectors exactly who accessed what — and when.
Native Active Directory, LDAP & SAML/OIDC sign-in
Automatic user provisioning & de-provisioning
Complete, time-stamped access audit trail
A live walkthrough built around your process. We reply within one business day.
YOUR USERS. YOUR DIRECTORY.
See KOŚA Active Directory in action.
A tailored walkthrough for your identity and access setup.
30-minute walkthrough · No obligation
Trusted by quality, regulatory & IT teams in pharma, biotech & medical devices
PharmaCorp
BioGenex
MediLabs
CuraVita
NovaPharm
BioTrust
DESIGNED TO SUPPORT
21 CFR Part 11
EU GMP Annex 11
SAML 2.0 / OIDC
SCIM provisioning
FROM MANUAL ACCOUNTS TO CENTRAL CONTROL
Access managed once.
Enforced everywhere.
Stop creating and removing accounts by hand in every system. Let your directory drive who can sign in and what they can do.
Single sign-on your team already knows
Users sign in with their company credentials through AD, Azure AD / Entra ID, Okta or any SAML/OIDC provider.
Roles mapped from your groups
Directory groups map to KOŚA roles, so permissions follow the person — by site, department or function.
MFA & password policy enforced
Apply your organisation’s MFA, session and password rules to every GxP module.
Access evidence ready for inspection
Every sign-in, role change and de-provisioning is recorded in a time-stamped audit trail.
40%
of the cost of legacy compliance suites
14
modules on one validated platform
8-10
weeks typical KOŚA implementation
30 min
focused walkthrough, no obligation
EVERY USER. A CLEAR LIFECYCLE.
Joiners, movers, leavers.
Handled automatically.
1
Connect your directory
Link Active Directory, LDAP or your SSO provider securely.
2
Map groups to roles
Align directory groups with KÓSA roles and site permissions.
3
Provision automatically
New starters get access on day one; leavers lose it immediately.
4
Review & prove access
Run periodic access reviews and export audit trails for inspectors.
On-premise Active Directory and LDAP, plus SAML 2.0 and OIDC providers such as Microsoft Entra ID (Azure AD), Okta and Google Workspace.
Does it work across all KOŚA modules?
Yes. One directory connection controls sign-in and roles across DMS, QMS, LMS and every other KOŚA module.
How does it support 21 CFR Part 11?
Unique user identification, enforced authentication and time-stamped access audit trails. Your team remains responsible for validation, procedures and regulatory compliance.
What happens when an employee leaves?
When the account is disabled in your directory, access to KOŚA is removed automatically and the change is logged.
✓
Thank You!
Your 1-Month Free Trial request has been received successfully.
Our team will contact you with the next steps.
Get 1 Month FREE on KOSA DMS & LMS
Simplify document control and GxP training with KOSA’s compliance-ready platform
Automate SOP approvals & version control
Track GxP training & employee competency
Stay audit-ready with traceable records
Request Your 1-Month Free Trial
Share your details and our team will contact you to set up your trial.
Your information will be used to process your request.